CertiK, a security firm, detected on April 13 that the Hyperbridge cross-chain gateway contract was hit by a vulnerability attack. The attacker used forged messages to bypass contract verification, successfully altered the administrator privileges of the Polkadot-bridged DOT token contract, and then illegally minted 1 billion bridged DOT tokens and fully dumped them in a single transaction. In the end, the attacker’s profit was only 108.2 ETH, worth approximately $237k.
Attack Mechanism: How Forged Cross-Chain Messages Obtain Administrator Control
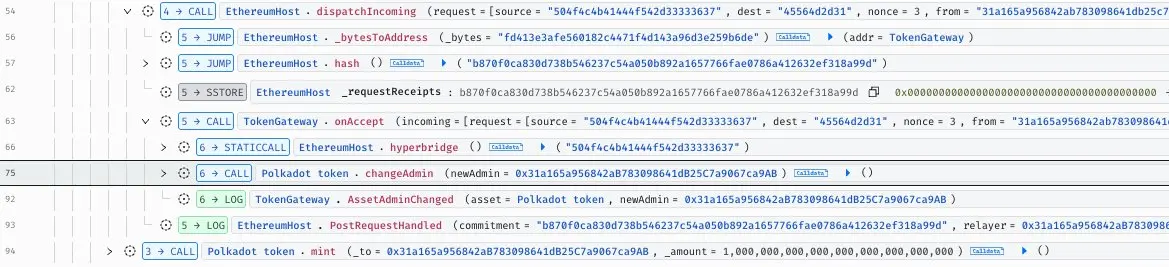 (Source: CertiK)
Hyperbridge is a cross-chain gateway protocol deployed on Ethereum that allows assets from networks such as Polkadot to circulate on Ethereum in the form of bridged tokens. According to CertiK’s monitoring, the attacker identified a message verification vulnerability in the contract. By constructing forged cross-chain messages to bypass the required legitimacy checks, the attacker successfully took control of the administrator for the bridged DOT token contract.
After obtaining administrator privileges, the attacker carried out unauthorized minting operations, creating 1 billion bridged DOT tokens out of thin air, and then immediately dumped all of them in a single transaction. The entire process—faked messages, altered the administrator, minted tokens, and liquidated positions—was completed on-chain. Lookonchain, an on-chain tracking organization, confirmed that the final proceeds from this transaction were only 108.2 ETH.
Why 1 Billion Tokens Only Netted $237k: The Brutal Math of Liquidity Traps
The most ironic detail in this attack is the huge gap between 1 billion tokens and $237k. Lookonchain data shows that before the attacker dumped the tokens, the quoted price of bridged DOT was about $1.22, implying a theoretical maximum arbitrage space of over $1.2 billion. However, the massive sell pressure from 1 billion tokens instantly exceeded the liquidity depth the chain could absorb. The token price crashed from $1.22 to nearly zero, and the vast majority of the newly minted tokens were essentially worthless.
This is a typical “liquidity trap”: attackers can create tokens, but they can’t create buyers.
Key Data Summary of This Attack
Attacked contract: Hyperbridge cross-chain gateway contract on the Ethereum chain
Attack method: Forged cross-chain messages to tamper with the administrator privileges of the bridged DOT token contract
Illegally minted amount: 1 billion tokens of bridged DOT on Ethereum
Token price before the dump: About $1.22; after the dump: nearly zero
Attacker’s actual profit: 108.2 ETH (about $237k)
Theoretical highest arbitrage: If liquidity were sufficient, theoretically could exceed $1.2 billion
Scope affected: Bridged DOT on Ethereum; Polkadot’s native chain is not directly affected
Important Distinction: The Security Boundary Between Bridged Assets and Native DOT on Polkadot
The target of this attack was the bridged DOT token contract deployed on Ethereum. In this incident, the Polkadot native main chain and its consensus mechanism for native DOT tokens were not directly attacked or affected.
Cross-chain bridges have long been one of the most concentrated areas of security risk in the DeFi ecosystem. The smart contracts that back bridged assets are typically deployed independently. Their security audit standards and monitoring mechanisms may differ from those of the native chain, enabling attackers to cause disruption by exploiting vulnerabilities in the bridged contracts without ever touching the main chain. Users holding bridged assets need to clearly recognize that the risks they bear come not only from the underlying main chain, but also from the contract security of the bridging infrastructure itself.
Frequently Asked Questions
What is Hyperbridge? What’s its relationship to Polkadot?
Hyperbridge is a cross-chain gateway protocol deployed on Ethereum. It allows assets from networks such as Polkadot to circulate on Ethereum in the form of bridged tokens. It is one of the infrastructure components that connects the Polkadot and Ethereum ecosystems, but in terms of technical architecture, it operates independently of the Polkadot native main chain.
The attacker minted 1 billion DOT. Why did they ultimately only profit $237k?
When the attacker dumped 1 billion bridged DOT tokens, the liquidity depth on the Ethereum chain was far too insufficient to absorb a sell order of such magnitude. The sell pressure instantly smashed the token price from $1.22 to nearly zero, causing the vast majority of the minted tokens to be barely sellable. Ultimately, only a tiny proportion could be sold in advance before the market collapsed, netting about 108.2 ETH in cash.
Did this attack affect DOT holders on Polkadot’s native chain?
According to CertiK’s analysis, the target of the attack was the bridged DOT contract on Ethereum. The Polkadot native main chain and native DOT token were not directly impacted. Investors holding DOT on the Polkadot main chain faced indirect market sentiment effects rather than direct security risks to underlying assets.


